

Product of the Day
AgentShield blocks rogue AI commands
A Cape Town-developed cybersecurity tool monitors automated AI activity and blocks suspicious database requests, writes GUIDO RUSSO.

An AI assistant tasked with summarising customer feedback could be tricked into attempting to delete a company’s database by malicious instructions hidden in that feedback. A South African-developed cybersecurity tool aims to stop such unauthorised actions before they reach business systems.
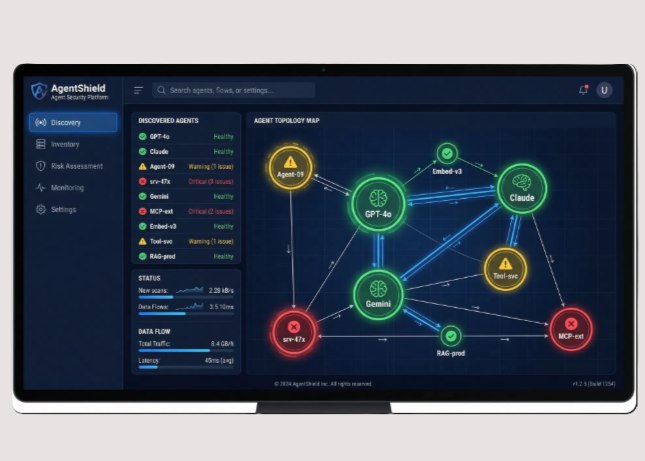
Cape Town technology company GovernX has developed Custos AgentShield, a security module within its broader Custos data protection platform. The software monitors autonomous AI agents, which are programs capable of carrying out tasks across applications, databases and other systems without human approval at every step.
AgentShield checks the commands these agents issue and restricts their access to approved functions. GovernX says the software can block attempts to delete or modify database records, limit how much information an AI assistant retrieves and interrupt suspicious network connections.
The platform supports AI development environments including Microsoft Copilot Studio, LangChain and AutoGen, which businesses can use to create automated assistants that interact with internal information.
A central feature is protection against prompt injection, a cyberattack in which malicious instructions hidden in documents, messages or other content attempt to redirect an AI assistant from its intended task.
GovernX illustrates this risk with a scenario on its website involving an AI assistant instructed to summarise a customer support ticket. After encountering malicious instructions, the assistant attempts to extract customer records. AgentShield is designed to recognise the unauthorised change in behaviour and terminate the database connection.
According to GovernX, AgentShield can interrupt suspicious connections in less than a millisecond. The company claims the network connection itself can be terminated in as little as 126 microseconds.
The company’s wider Custos platform includes a separate ransomware protection module, Custos ShannonEntropy. This technology monitors database storage for sudden increases in mathematical randomness, which can indicate that ransomware is encrypting information.
When suspicious encryption activity is detected, GovernX says the module can terminate associated network connections through controls operating within the computer’s operating-system kernel. The company claims response times below 500 milliseconds.
Another module, Custos SafeHarbor, uses cryptographically signed records to create tamper-evident logs of security activity. These records can help organisations demonstrate which safeguards were operating during an incident and support subsequent investigations.
Data sovereignty forms part of GovernX’s approach.
“Zero telemetry leaves South African borders,” GovernX founder and CEO Brandon Fortune told Gadget. “All processing, modeling, and audit proofs reside exclusively within Azure South Africa North.”
The company’s current product documentation details on-premises and air-gapped deployments that can operate without an internet connection. Such configurations are aimed at organisations handling sensitive information, including financial institutions, telecommunications providers and critical infrastructure operators.
GovernX says the company is engaging systems integrators and state research bodies about deployments across South African critical infrastructure.
* Visit the GovernX website here.