

Cybersecurity
SA struggles to bounce
back from ransomware
New research by Sophos shows recovery from attacks remains slow, and AI is adding new security problems, writes JASON BANNIER.

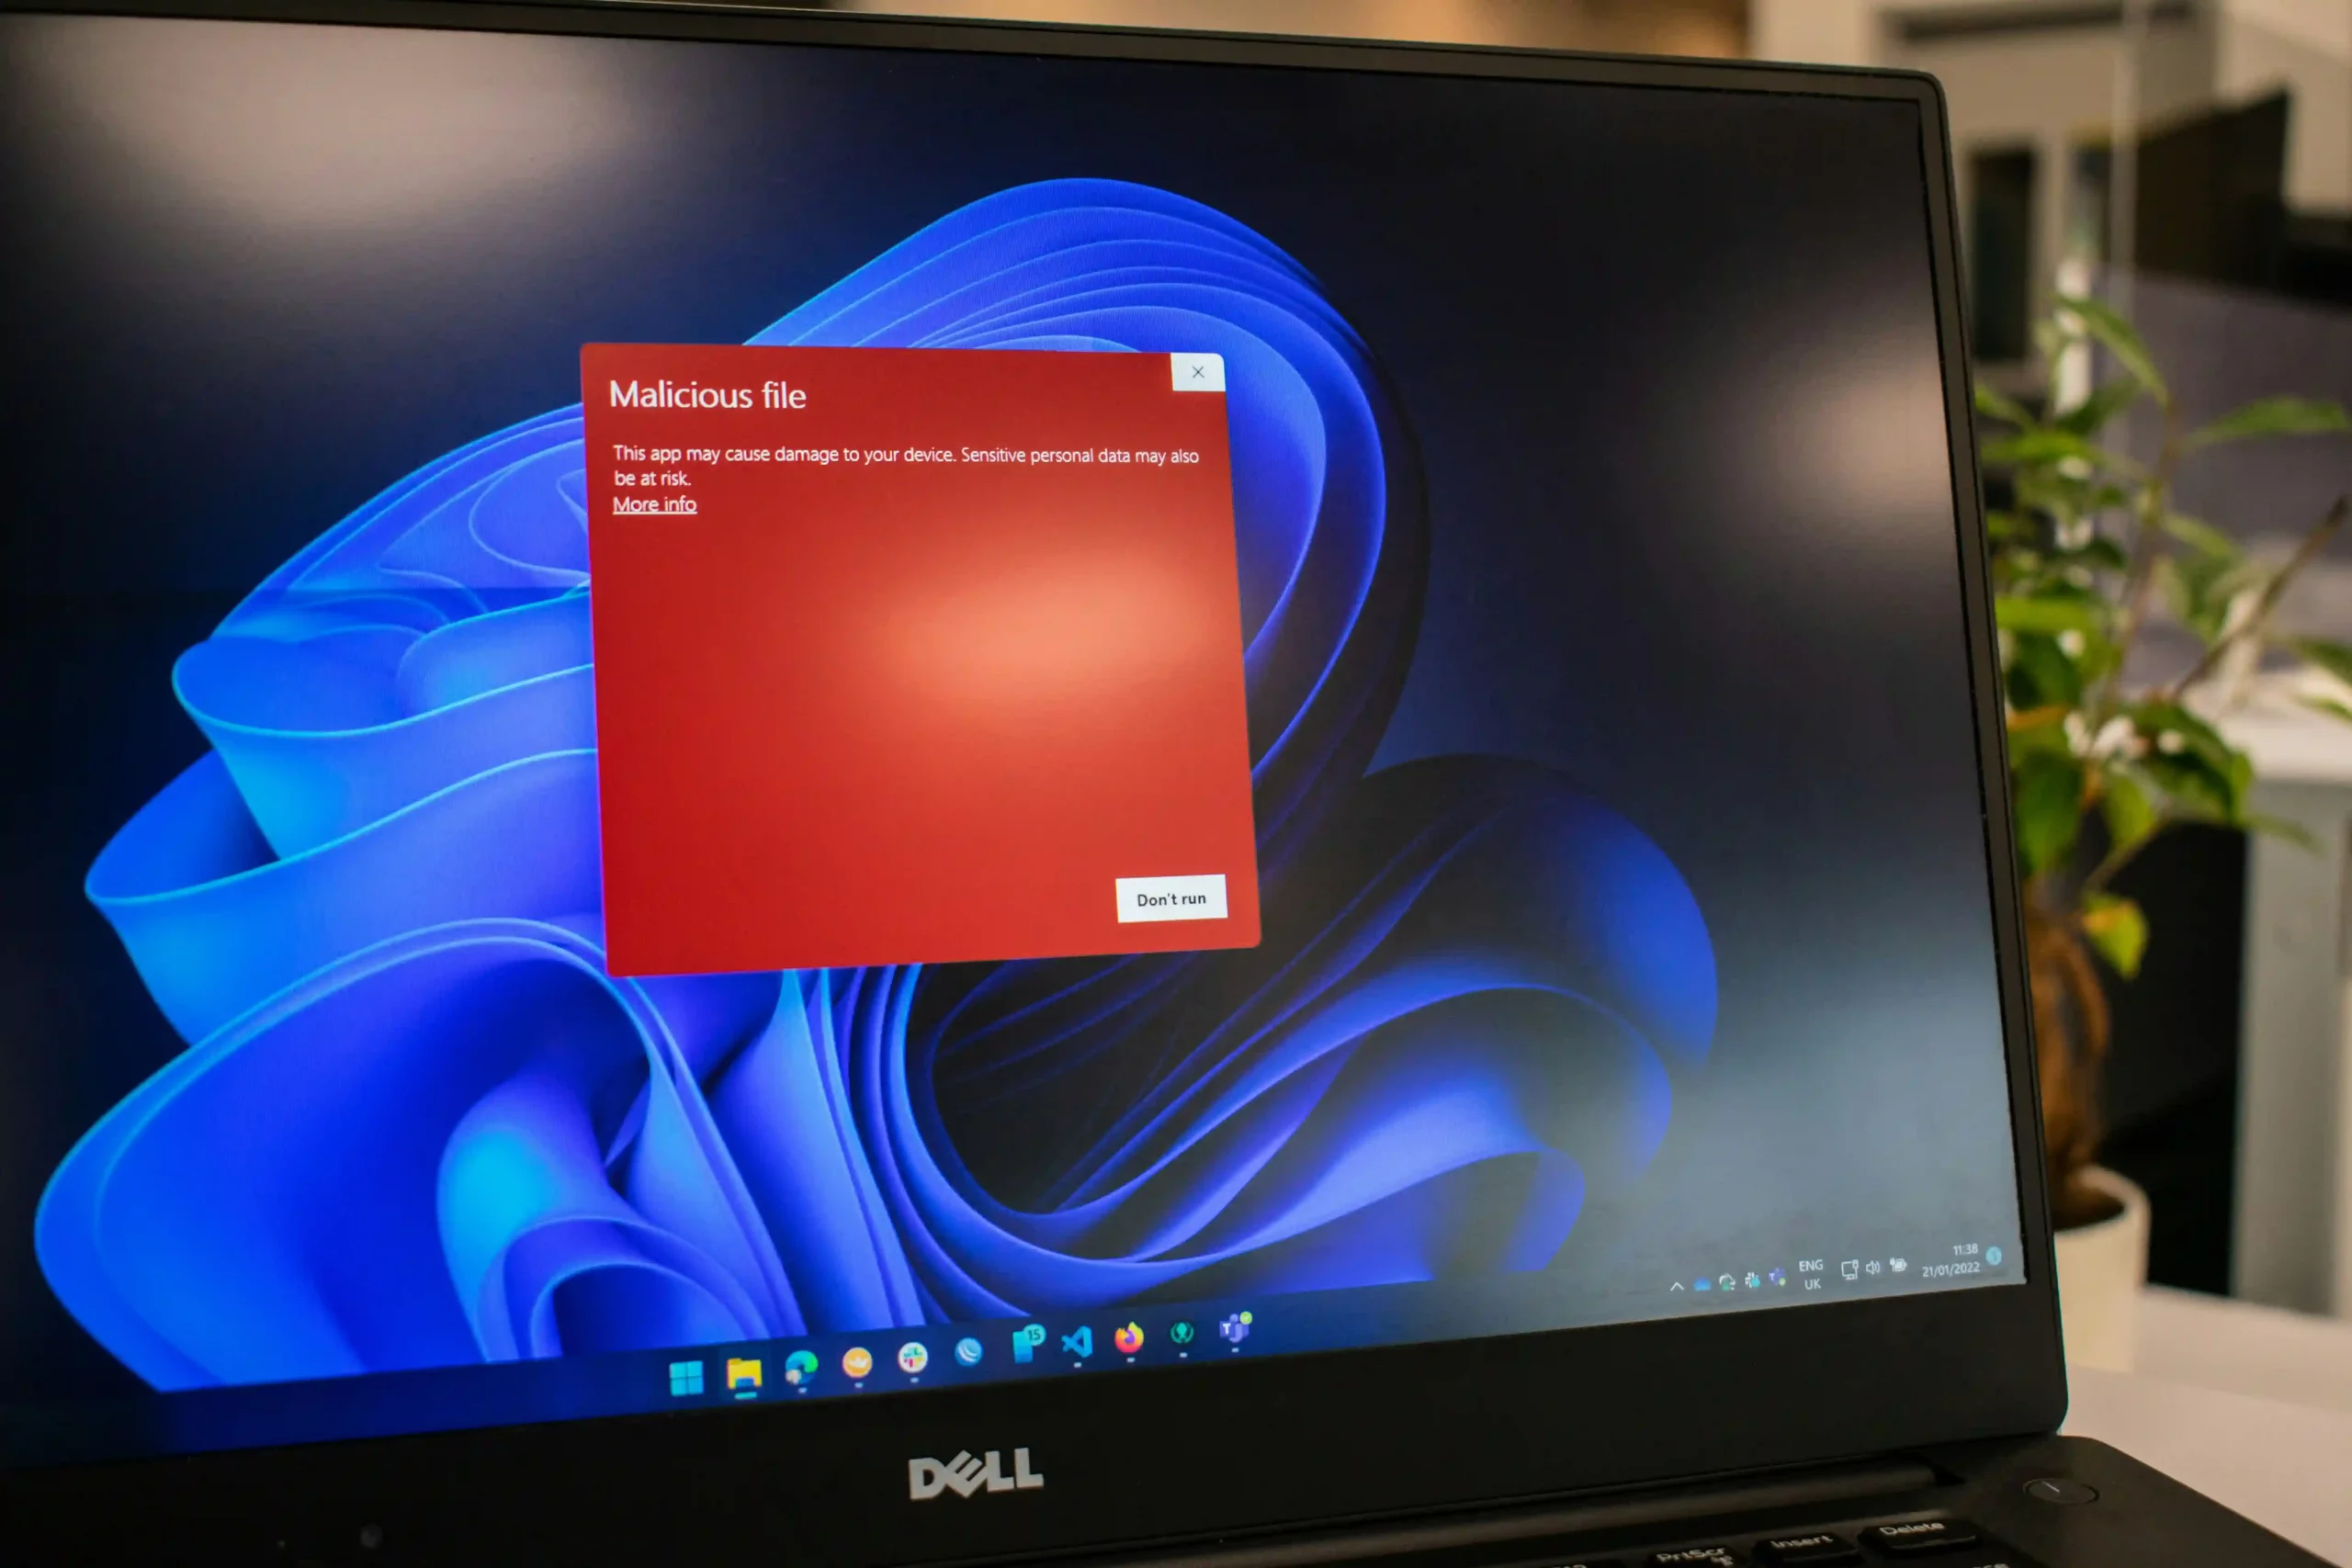
South African organisations are getting better at recovering data after ransomware attacks. However, returning operations to normal is proving far more challenging.
A new Sophos report, The State of Ransomware 2026, found ransomware encrypted data in 63% of local incidents over the past year. This means attackers scrambled files or other information so organisations could no longer use them normally. The rate increased from 60% in the previous research and was above the 56% global average.
Of the South African organisations whose data was encrypted, 99% eventually recovered the information. Yet, only 40% recovered from the overall attack within a week. This was the lowest rate among countries surveyed.
The average recovery cost exceeded R17-million, excluding ransom payments.
The findings arrive as businesses face another security challenge. Employees are adding chatbots, coding assistants and other AI services to daily work, while attackers are using the same technology to speed up parts of cyberattacks.
For Sophos, the two sides increasingly meet around access to company systems and information.
“We haven’t seen anything that’s unknown with AI,” Pieter Nel, Sophos regional head for Southern African Development Community, told Gadget. “It’s just enhanced in speed and process.”
He said bots and AI tools could automate commands and speed up parts of an attack, but criminals still depended on vulnerabilities and other weaknesses to gain access.
“Ultimately it still comes back to exploit techniques.”
The report supports that point. Compromised credentials were the most common technical cause, accounting for 27% of incidents. These are legitimate usernames, passwords or other login details that have fallen into the wrong hands, allowing criminals to enter a system while appearing to be authorised users.
Exploited vulnerabilities followed at 25%, meaning attackers took advantage of security flaws in software or systems. Malicious emails accounted for another 22%.
The same acceleration can already be seen in AI-assisted malware, where large language models have been used to help generate or alter malicious code. The Sophos report suggests South African organisations have no shortage of existing gaps to close.
Almost half of respondents (47%) said inadequate protection contributed to the ransomware incident. This was the highest proportion recorded among the surveyed countries.
A lack of people or cybersecurity capacity was cited by 43%, while 42% said attackers exploited a security gap the organisation already knew about.
Identity was particularly closely tied to ransomware. Of the 135 South African organisations surveyed, 85% said the ransomware attack was the same event as their most significant identity attack during the year. The global figure was 67%.
An identity attack targets the accounts and permissions used to establish who someone is inside a company system. A stolen employee login can therefore give a criminal legitimate-looking access before ransomware is deployed.
“Compromised credentials allow criminals to appear as legitimate users, while unpatched vulnerabilities and exposed systems provide additional routes into the business,” Nel said in the report.
AI introduces another access problem from inside the organisation. Employees may use AI services that have never been approved or assessed by the security team. The practice, called shadow AI, can range from using an unapproved chatbot to uploading company documents or connecting outside AI tools to workplace systems.
Nel describes a market with “too many tools” available to employees.
“The problem is you can’t always take control what the user is doing with AI,” Nel told Gadget.
Sophos is preparing AI Defense, a security add-on designed to show companies which AI applications employees are using and let administrators apply rules to those services. A company can approve selected platforms while warning or blocking users who turn to others.
“That means, as a business, you can now control what users can do in AI and what platform.”
AI Defense is an optional add-on within Sophos Fusion, the connected cybersecurity system launched earlier this year. The product is expected to become available in October.
“You can build a proper cybersecurity policy on AI and best practice for the users.”
Company data can escape through AI even when nobody is deliberately trying to steal anything.
Recent Check Point research found high-risk generative AI prompts at 86% of organisations regularly using the technology. One in every 43 prompts sent from enterprise networks presented a risk of data exposure, while organisations used seven AI tools on average.
That risk does not require a cyberattack. An employee can paste confidential information into a chatbot, upload an internal document for help with a presentation or provide company data while drafting a response. The task may be legitimate, while the AI service receiving the information sits outside company policy.
A more deliberate attack can turn the AI system itself against the user. Nel pointed to malicious prompts hidden inside emails or other content.
“We’ve seen some mails being populated with hidden white space in the back end with prompts being loaded.”
The technique, known as indirect prompt injection, places instructions inside material that an AI assistant later reads. The employee may see an ordinary email or document, while the AI encounters a hidden command as part of the same content.
Nel said an AI agent can then read those prompts when processing the material.
The risk becomes greater when an AI assistant has permission to search email, company documents or cloud services. A malicious instruction does not need to break into each system separately if the AI already has legitimate access on behalf of the user.
One example was EchoLeak, a vulnerability in Microsoft 365 Copilot disclosed in 2025. A specially crafted email could hide instructions that influenced Copilot and, under certain conditions, expose limited internal data the user already had permission to access.
AI Defense is intended to give security teams visibility over such AI activity alongside the other systems they already monitor.
Nel said the product links into a data lake, a central store where large volumes of security information can be brought together and compared.
Sophos can combine that information with endpoint detection and response, which monitors individual computers and devices, and extended detection and response, which connects security signals across a wider company environment. Managed detection and response adds specialist teams that investigate and respond on behalf of customers.
The recovery data shows why security teams need a fuller picture.
South African organisations have made clear progress in recovering encrypted information. Backup use rose from 35% in the previous report to 54% this year, reducing reliance on criminals to restore data.
The proportion that paid a ransom and recovered data fell from 71% to 58%. Data theft also declined from 39% of attacks involving encryption to 27%.
Criminals were demanding less as well. The median ransom demand dropped 57%, from R16-million to R6,8-million, while the median payment fell 28% to almost R5-million.
Those improvements did not make the disruption disappear.
Six in ten South African organisations needed longer than a week to recover fully. Among those where data was encrypted, 52% reported increased pressure from senior leaders and 36% reported greater anxiety or stress about another attack.
Almost a quarter said team leadership had been replaced.
The report shows gains in recovery, but ransomware is still causing significant disruption. More victims are recovering data through backups and fewer depend on ransom payments, yet encryption is affecting a greater share of attacks and recovery remains slow.
AI adds pressure from both directions. Criminals can use the technology to move faster through existing attack methods, while employees are giving more AI services access to company information.
* Download the ‘The State of Ransomware 2026’ report here.
* Jason Bannier is a data analyst at World Wide Worx and deputy editor of Gadget.co.za. Follow him on Bluesky at @jas2bann.